Making AI agents safe to trust with real permissions.
Staff Security Engineer working on AI-agent security, Zero Trust, and cloud security. I write the weekly Securing the Agentic Stack newsletter and have published four peer-reviewed AI-security papers. I build security that’s invisible and infrastructure that’s boring — today as the first security engineer at Parafin, which has funded $3B+ to 60,000+ small businesses and is joining Stripe. Papers: EmbedGuard, GenOps, RuntimeGuard-AI, and TriArchitect (2026), plus two arXiv preprints (PerceptFence, The Acknowledgment Point Is the System). Speaker at Conf42 DevOps 2026, Conf42 LLMs 2026, and CIMA 2026. Full Member, Sigma Xi. Fellow, IICSPA and Hackathon Raptors. Building mission-critical systems since 2011 across Parafin, Meta, Wayfair, JPMorgan Chase, and American Express.

My Story

I work on one problem: making AI agents safe to trust with real permissions — the identity, Zero Trust, and cloud-security plumbing underneath them. My journey in tech began with a simple question: “How can this be better?” It’s a question that has taken me from writing COBOL adapters for American Express across three continents to building Zero Trust and AI-agent security for embedded lending at scale.
Today I’m a Staff Security Engineer — the first security engineer at Parafin, which has funded $3B+ to 60,000+ small businesses and is joining Stripe. I built its vulnerability-management program from zero, ran the SOC 2 Type II program end to end, and own AI governance and MCP tool-access security. I’ve published four peer-reviewed AI-security papers in 2026 (EmbedGuard, GenOps, RuntimeGuard-AI, TriArchitect), posted two arXiv preprints (PerceptFence and The Acknowledgment Point Is the System), spoken at Conf42 DevOps, Conf42 LLMs, and CIMA 2026, write the weekly Securing the Agentic Stack newsletter, and earned Full Membership in Sigma Xi — The Scientific Research Honor Society — and Fellowships in IICSPA and Hackathon Raptors.
I thrive on turning complex distributed systems into reliable (and slightly boring) platforms. My goal is to automate the pain points away and build security so seamless you forget it’s there. Whether I’m sketching system diagrams, mentoring engineers (50+ so far), or debugging a gnarly distributed trace at 2am, I’m always searching for the next puzzle to solve.
Awards, publications & memberships
International awards
Gold Laureate — Aureum Technology Awards Season 3 (NLP Achievement Award; reference TEC-26-12296), Aureum International Awards Council. Season 3: 4,067 applications received, 1,082 advanced to full assessment, 213 laureates after multi-phase expert evaluation (per program materials and press). Media: Markets Insider — Season 3 results.
Scholarly & research publications
Four peer-reviewed papers published in 2026 — all open access and DOI-registered — plus two arXiv preprints (not peer reviewed).
EmbedGuard — Cross-Layer Detection and Provenance Attestation for Adversarial Embedding Attacks in RAG Systems — IJCESEN, Vol 12 No 1, pp 589–602, 2026. DOI 10.22399/ijcesen.4869 · Implementation (GitHub). The paper reports a 94.7% detection rate on optimization-based attacks at 51 ms mean overhead, evaluated on a 500K-embedding production-scale system.
GenOps — A Governance-First Architecture for Embedding Generative AI into CI/CD Pipelines — JISEM, Vol 11(1s), pp 1518–1539, 2026. DOI 10.52783/jisem.v11i1s.14322. Companion talk at Conf42 DevOps 2026. The paper reports a 55.7% reduction in median deployment cycle time with zero safety-policy violations across 15,847 deployments.
RuntimeGuard-AI — Scalable Tamper-Evident Accountability for High-Risk AI Systems Under the EU AI Act — JoCAAA (Journal of Computational Analysis and Applications, Eudoxus Press), Vol 35 No 1, pp 1074–1090, 2026. DOI 10.48047/jocaaa.2026.35.01.87. Companion talk at Conf42 LLMs 2026. The paper presents an open-source compliance architecture for EU AI Act Article 14, using Groth16 zero-knowledge proofs at 2.3–4.1% latency overhead.
TriArchitect — A Shared-State Multi-Agent Framework for Safe Java Code Migration — IJCISIM (International Journal of Computer Information Systems and Industrial Management Applications, Cerebration Science Publishing), Vol 18 No 18s, pp 739–751, published 19 August 2026. DOI 10.70917/ijcisim-2026-4917 · PDF. A shared-state multi-agent architecture — Typed Migration Graph plus a Validator-Veto Protocol — for state-aware, safety-checked Java legacy migration.
Preprints (arXiv, not peer reviewed):
The Acknowledgment Point Is the System — Durable Policy-Decision Receipts for AI Audit Evidence — sole-author preprint, arXiv cs.CR, Aug 2026. arXiv:2608.17176 · DOI 10.48550/arXiv.2608.17176 · Code (RuntimeGuard-AI v2.0.0). Rebuilds RuntimeGuard-AI around durability/latency trade-offs, with Ed25519-signed policy-decision receipts and chained Merkle-epoch attestation.
PerceptFence (preprint, with Asmita Negi, equal contribution) — Content-Mediation Architecture and Deterministic Coverage for Screen-Share AI Assistants — v0.4.0 (Sep 2026) tests it on the real screen-share path: 480 held-out developer-support screens rendered in Chrome and read back by OCR, with the rules frozen before testing. It neutralised 889 of 968 leaked secrets and PII values (0.918), against 0.581 for Microsoft Presidio and 0.179 for gitleaks. Zenodo v0.4.0 DOI 10.5281/zenodo.23004093 · all-versions DOI 10.5281/zenodo.21150725 · GitHub release v0.4.0 · Preprint arXiv:2609.34027 · DOI 10.48550/arXiv.2609.34027 (cs.CR, Sep 2026; not peer reviewed). Research artifact on Zenodo and GitHub.
Technical writing & community reach
Writing on LinkedIn, Dev.to, Hashnode, and the Securing the Agentic Stack newsletter — agentic AI security, MCP risk, RAG pipelines, Kubernetes, Kafka, and distributed systems. Representative titles include Your Agent Can’t Tell What It Was Told From What It Read (2026) and Prompt Engineering vs Context Engineering vs Reasoning Engineering (2026).
Speaking
Conf42 LLMs 2026 — invited talk: RuntimeGuard-AI: Cryptographic Compliance for High-Risk AI Pipelines — recording (YouTube) · verified speaker certificate.
Conf42 DevOps 2026 — invited talk: GenOps: A Governance-Driven Model for Safe, High-Velocity AI in CI/CD Pipelines — session page · recording (YouTube).
CIMA 2026, NIT Puducherry — invited talk: Governing Generative AI in Production: Building Trustworthy and Secure AI Systems — talk page.
Open source
NVIDIA/garak — authored the adaptive-attacks probe for the LLM red-teaming framework (PR #1742, merged; shipped in v0.16.0).
Paperclip — three merged PRs to the agent-orchestration platform: silent-process watchdog (#5017), loopback routing fix (#5102), and AWS Fargate runbook (#3897).
hermes-cursor-acp and hermes-antigravity-oauth — MIT-licensed Hermes Agent provider plugins, published to npm with OIDC provenance.
FAANG — interview-prep algorithms & patterns (1,880 GitHub stars, 489 forks as of Jul 2026).
EmbedGuard — reproducible RAG-security research framework (Docker, tests, benchmarks).
PerceptFence — DOI-backed research artifact for screen-share AI assistant content mediation, with a Chrome + OCR evaluation harness (v0.4.0) · arXiv:2609.34027.
faang-system-design — curated system-design notes (179 stars, 41 forks as of Jul 2026).
Fellowships & professional memberships
Fellow, Hackathon Raptors — UK Community Interest Company 15557917; peer-elected fellowship for sustained builder / hackathon achievement (Fellow #14975).
Fellow (FIICSPA), International Institute of Computer Science Professional Association (IICSPA).
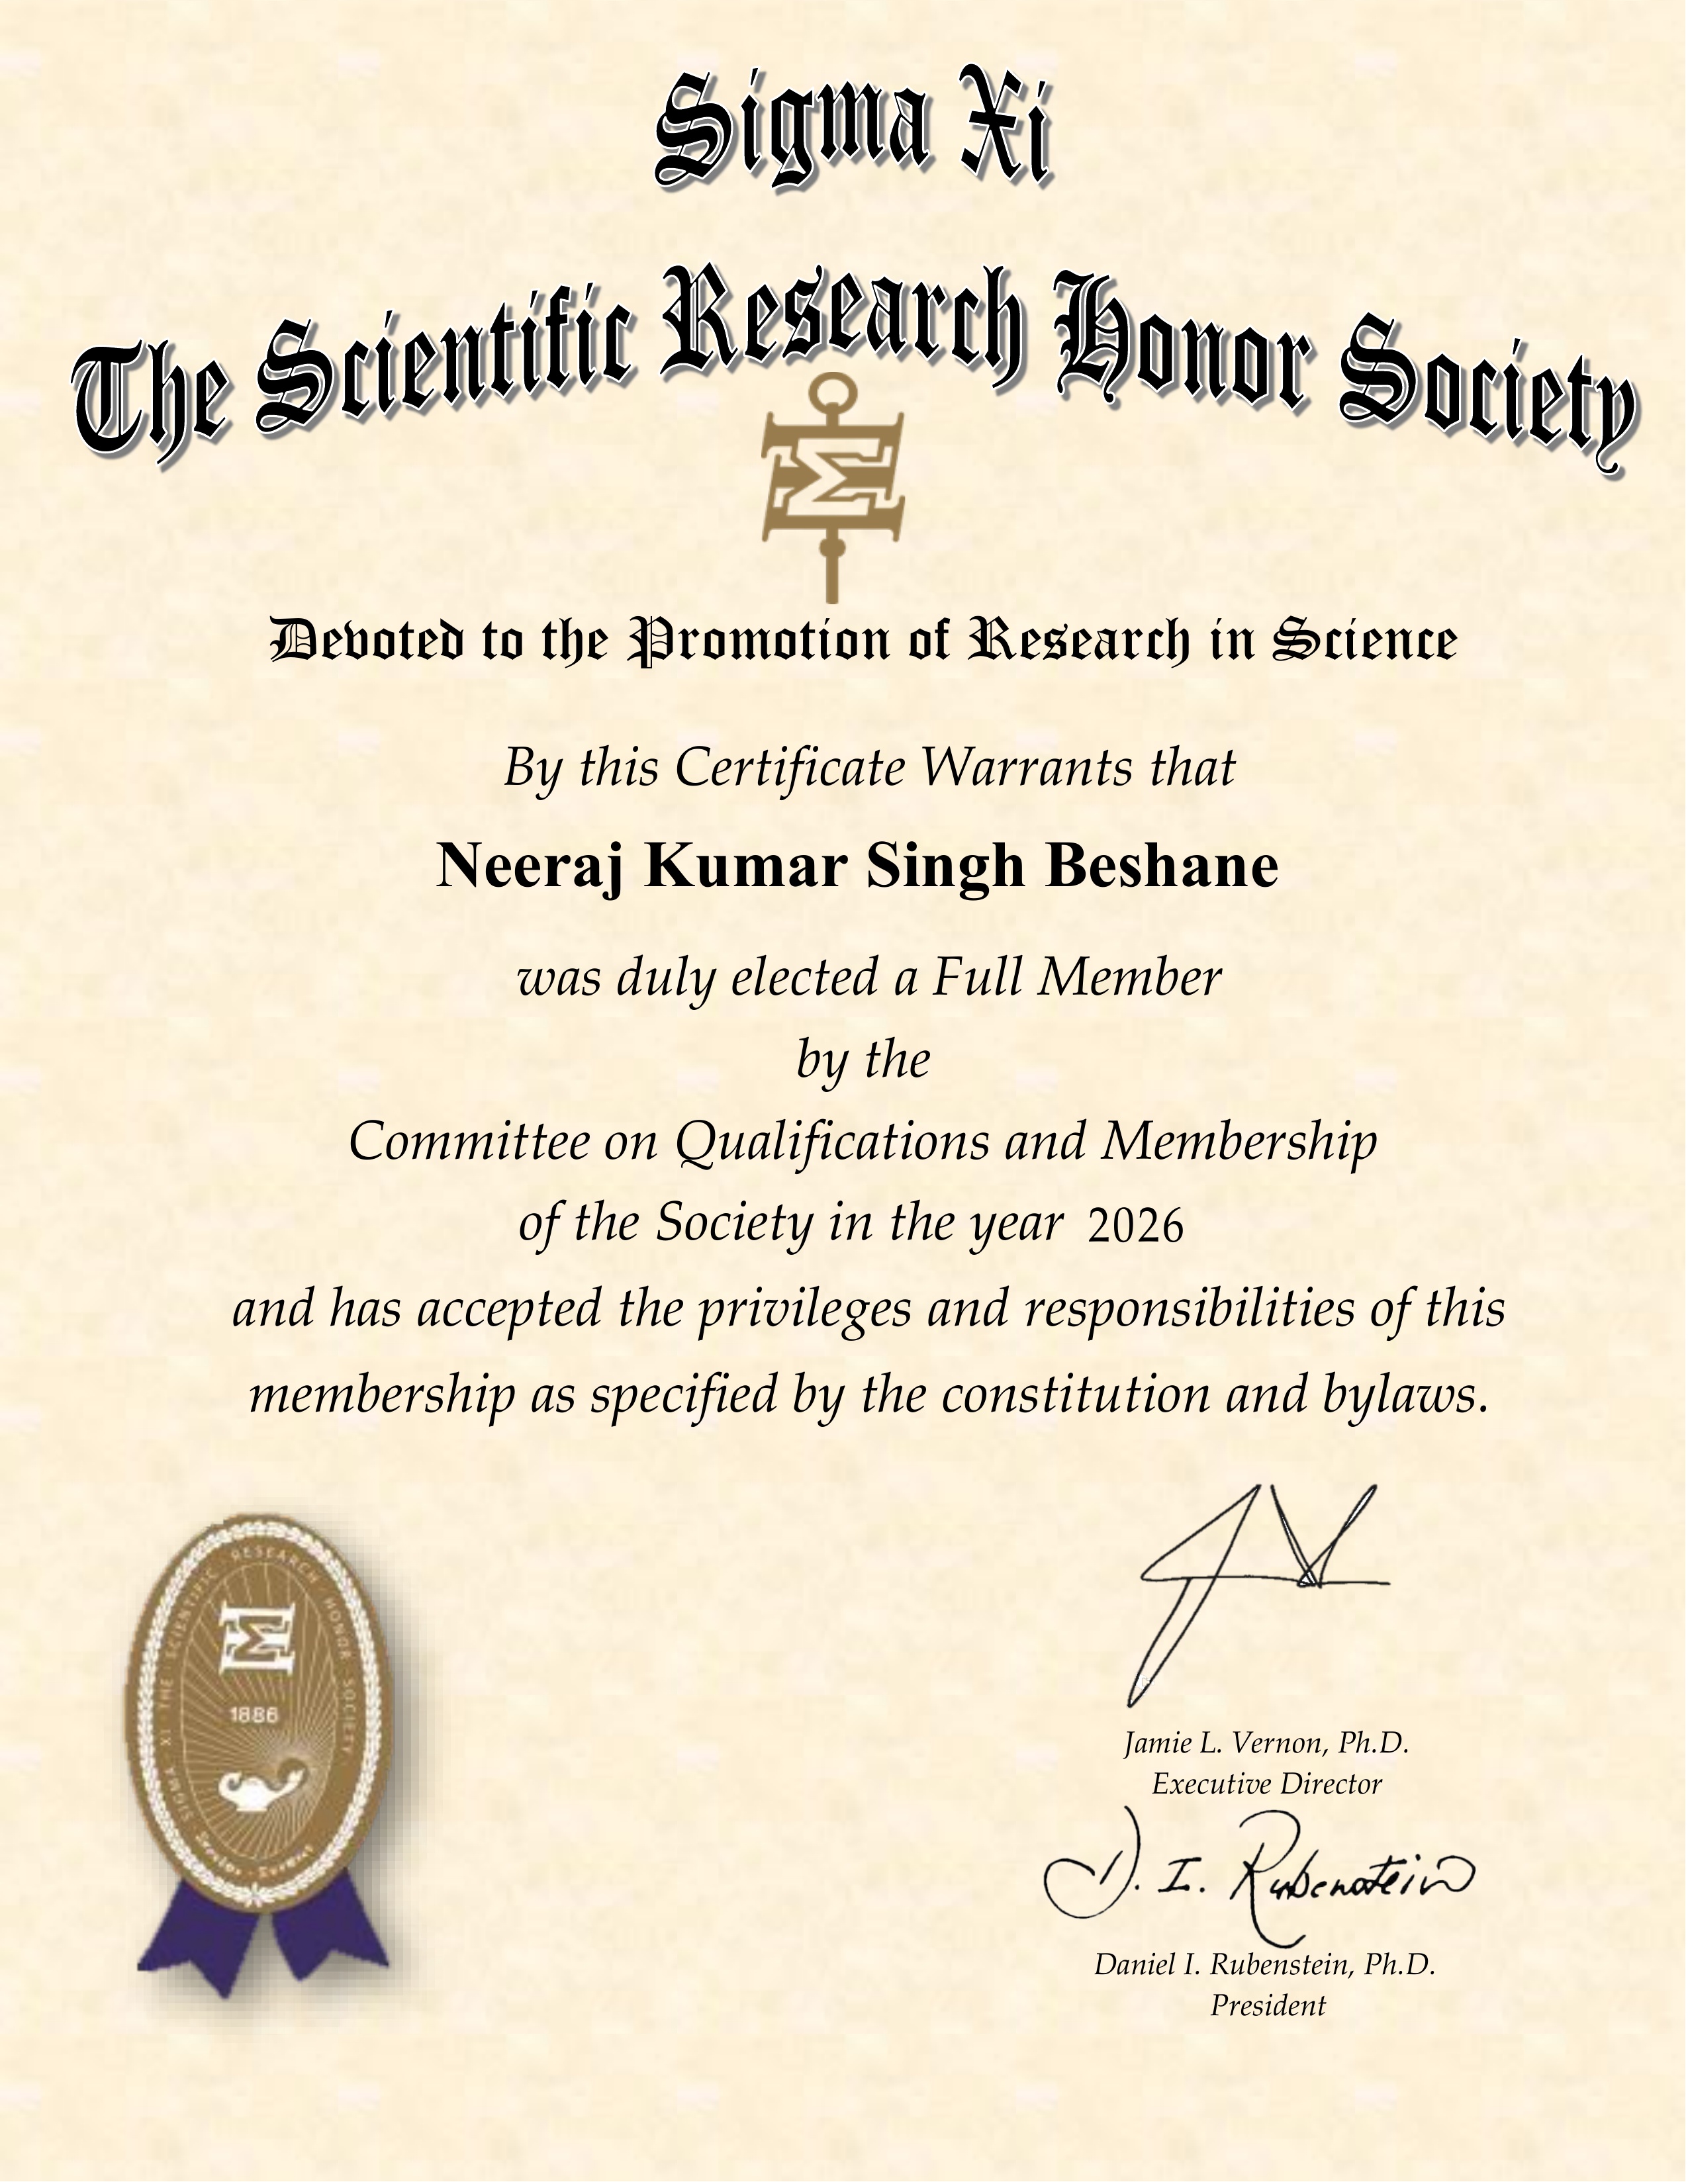
Full Member, Sigma Xi — The Scientific Research Honor Society, inducted Mar 2026. View membership certificate (JPG).
Member, IEEE.
Researcher ID: ORCID 0009-0002-2125-1805.
Peer review & service
Peer reviewer, Journal of Open Source Software (JOSS) — reviews of open-source research software submissions.
Mentor and judge, Apart Research Global South AI Safety Hackathon 2026 — public roster and organizer letter on file.
Other
- Google Developer Program (beta) · Google I/O 2023 attendee.

Architecting Simplicity, Engineering for Growth
I specialize in making complex systems secure, scalable, and reliable. Here’s how I help organizations thrive.

AI-Agent Security & Research
I secure AI agents and LLM systems — AI governance, MCP tool-access controls, and adversarial testing — and publish the research behind it: RAG embedding attacks (EmbedGuard), CI/CD governance for GenAI (GenOps), tamper-evident AI accountability (RuntimeGuard-AI), and screen-share content mediation (PerceptFence).

Zero Trust & Security Infrastructure
I design and implement Zero Trust security architectures — from identity and access management to policy-as-code enforcement and PII governance — helping organizations protect critical infrastructure without slowing down engineering velocity.

Cloud Security & Platform Engineering
I design and build resilient, scalable infrastructure on AWS and GCP using Kubernetes, Terraform, and modern cloud-native tools. I focus on paved-road platforms that developers can trust under production pressure.
Software Supply-Chain Security & Distributed Systems
I architect event-driven microservices and CI/CD platforms that handle millions of requests. I help teams embed security into every layer of the development lifecycle, enabling speed and safety simultaneously.
Experience & Education
Staff Security Infrastructure Engineer building secure, scalable, and reliable systems since 2011 across fintech, e-commerce, AR/VR, and financial services.
Bachelor of Technology — Electrical & Electronics Engineering
RVR JC College of Engineering, Guntur, Andhra Pradesh, India. Graduated with First Class distinction.
Parafin (Dec 2025–Present) — Staff Security Infrastructure Engineer
First security engineer at Parafin, which has funded $3B+ to 60,000+ small businesses and is joining Stripe. Built the vulnerability-management program from zero (policy, asset tiering, priority matrix, SLA engine). Ran the SOC 2 Type II 2026 program end to end (12 workstreams, 86 controls). Took BC/DR from expired to exercised with a live single-AZ production failover and zero customer impact. Set the org-wide AWS security baseline (tamper-proof CloudTrail with 7-year Object Lock, Security Hub, root MFA) and led the company’s first production TLS 1.3 migration. Designed OIDC + PKCE single sign-on for partner integrations and an identity/authorization map across four identity planes. Leads AI governance and MCP tool-access security, built a multi-agent design-review framework used on real ERDs, and is DRI for the annual third-party penetration test and the vendor security review program.
Meta — Reality Labs (Jun 2024–Dec 2025) — Staff Software Engineer
Build and software supply-chain infrastructure for Quest headsets and Ray-Ban Meta glasses. Tech lead for the Reality Labs CI/CD modernization: 200+ services onboarded through automated migrations with zero production incidents, P50 build time cut 35% and P95 cut 42%. Built the Unified Build Model metadata service, the source of truth for AR/VR build artifacts: 450M+ requests/day and 99% fewer build-tracking failures. Caching and trigger optimization reclaimed 22,000+ compute-hours a month. Built a GenAI migration assistant that removed 95% of manual migration effort. Mentored 6 senior engineers, 3 of whom were promoted to Staff within 12 months.
Raymond James (Apr 2024–Jun 2024) — Lead Software Development Engineer
Led a team of 8 engineers on the document-generation and digital-signature platform behind client onboarding across wealth management and corporate banking: Spring Boot microservices for PDF generation, e-signature integration and workflow orchestration, scaled on Docker and Kubernetes on AWS.
Wayfair (Jan 2022–Mar 2024) — Technical Architect
Security Development team. Built the DevSecOps platform adopted by all 15 Wayfair business units as the company-wide security standard: 50M+ security checks a month and a Kubernetes policy-as-code engine at a 3% false-positive rate. Architected Wayfair’s first unified OAuth 2.0 identity service: 125M+ API calls a week at 99.97% uptime. Cut security incident response time 40%. Mentored 20+ engineers (8 promoted to senior/staff).
JPMorgan Chase — CIB (Mar 2019–Dec 2021) — Senior Software Engineer
Electronic Specialty Accounts Portal (ESAP), Corporate & Investment Bank: the client-facing portal JPMorgan escrow clients use to open accounts, transfer funds and issue checks. Joined the team through Mphasis in March 2019 and became a JPMorgan employee in July 2021; by the end I was the portal’s core platform and security lead.
American Express — via TCS (Dec 2011–Mar 2019) — Senior Software Developer
Tata Consultancy Services consultant on American Express systems. Re-architected the monolithic International Insurance Services claims application into 5 Java 8 / Spring Boot 2.0 microservices; earlier supported Card Processing on IMS/DB2 mainframes and migrated International Membership Rewards logic from COBOL to Java across 30 markets. Worked in Bangalore, Montevideo (Uruguay) and Phoenix.

Engineering Superpowers
Building mission-critical systems since 2011 has sharpened a broad toolkit. Here are the areas where I bring the most value — from security architecture to AI/ML systems to distributed infrastructure.